

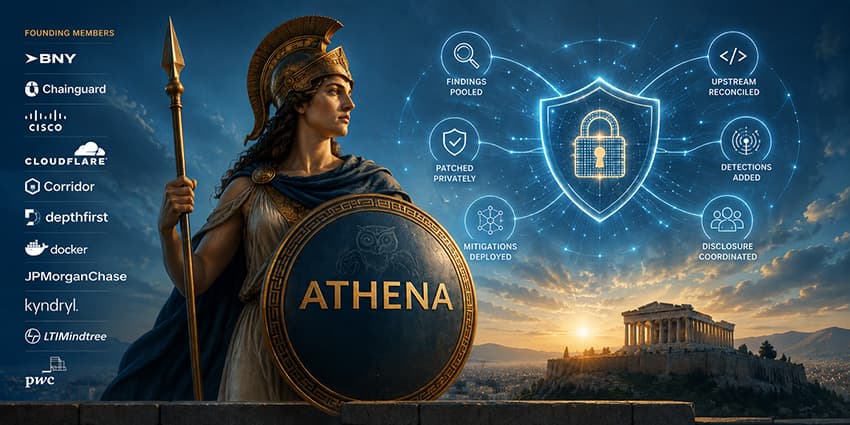
As frontier AI models accelerate the discovery of software vulnerabilities, a coalition of more than two dozen organizations has launched Athena, an initiative aimed at finding, fixing and mitigating security flaws in open-source software before attackers can weaponize them.
Led by Chainguard and backed by organizations including BNY, Cisco, Cloudflare, Corridor, depthfirst, Docker, JPMorganChase, Kyndryl, LTIMindtree, and PwC, Athena is designed to address the reality that AI systems can now identify vulnerabilities at a speed that traditional disclosure and remediation processes were never designed to handle.
Concerns around the capabilities of frontier AI models have intensified in recent weeks, reflected in the U.S. government's decision to restrict public access to Anthropic’s Mythos and Fable AI models over concerns about potential risks to critical infrastructure.
“The gap between a vulnerability being discovered and being exploited has collapsed from years to hours, and a growing share of exploits are weaponized before the bug is ever publicly disclosed,” Chainguard stated.
“Meanwhile, the critical software underneath everything is often maintained by one or two volunteers who are already buried in low-quality scanner noise. Coordinated disclosure was built for a world where finding a serious flaw took weeks and the targets were few. That world is gone.”
The Patch Window Is Collapsing
Vincent Danen, Vice President of Product Security at Red Hat, recently told CX Today in an interview that the shrinking patch window is forcing organizations to rethink long-established security operations.
“People who are used to a patch window have to learn to be nimble, because you may have to patch tomorrow and the day after, in addition to your regular patch cycle."
Athena aims to help organizations adjust to the new reality by operating as a shared platform for coordinating vulnerability response across the software ecosystem.
“Left alone, the default outcome is fragmentation: every cloud, vendor, and security team quietly forking the same critical libraries with its own patch set, and no shared truth about what's actually fixed. That is slower, weaker, and more dangerous for everyone,” Chainguard stated.
Coalition members contribute findings generated through advanced AI programs they have access to, including Anthropic's Project Glasswing and OpenAI's Daybreak. Those findings are then pooled, correlated, validated and reconciled against existing upstream activity before coordinated remediation efforts begin.
According to Chainguard, the coalition combines multiple layers of defense. Chainguard privately develops and distributes patches, infrastructure and network providers deploy mitigations ahead of disclosure, and cybersecurity partners create detections and signatures, while coalition members coordinate responsible disclosure with upstream maintainers.
In a LinkedIn post announcing the initiative, Chainguard CEO Dan Lorenc positioned Athena as an alternative to a fragmented future in which organizations struggle to independently maintain competing security fixes.
"Athena runs a shared, active platform that takes each vulnerability through its full lifecycle end to end. Within it, a clearinghouse pools and correlates findings from every member. Around that, Athena stacks independent layers of protection so that coverage exists even where a clean patch does not yet, and stays on every flaw until a durable upstream fix is in place."
The model is intended to create ecosystem-wide benefits from individual discoveries.
"That means a vulnerability one member discovers gets remediated and pushed upstream, becoming a fix the entire ecosystem inherits, often before disclosure."
“And for the parts of the world that can't patch on an attacker's timeline, partners who sit in front of much of the internet push mitigations out ahead of disclosure, blocking the issue for people who never knew there was anything to block,” Lorenc wrote.


