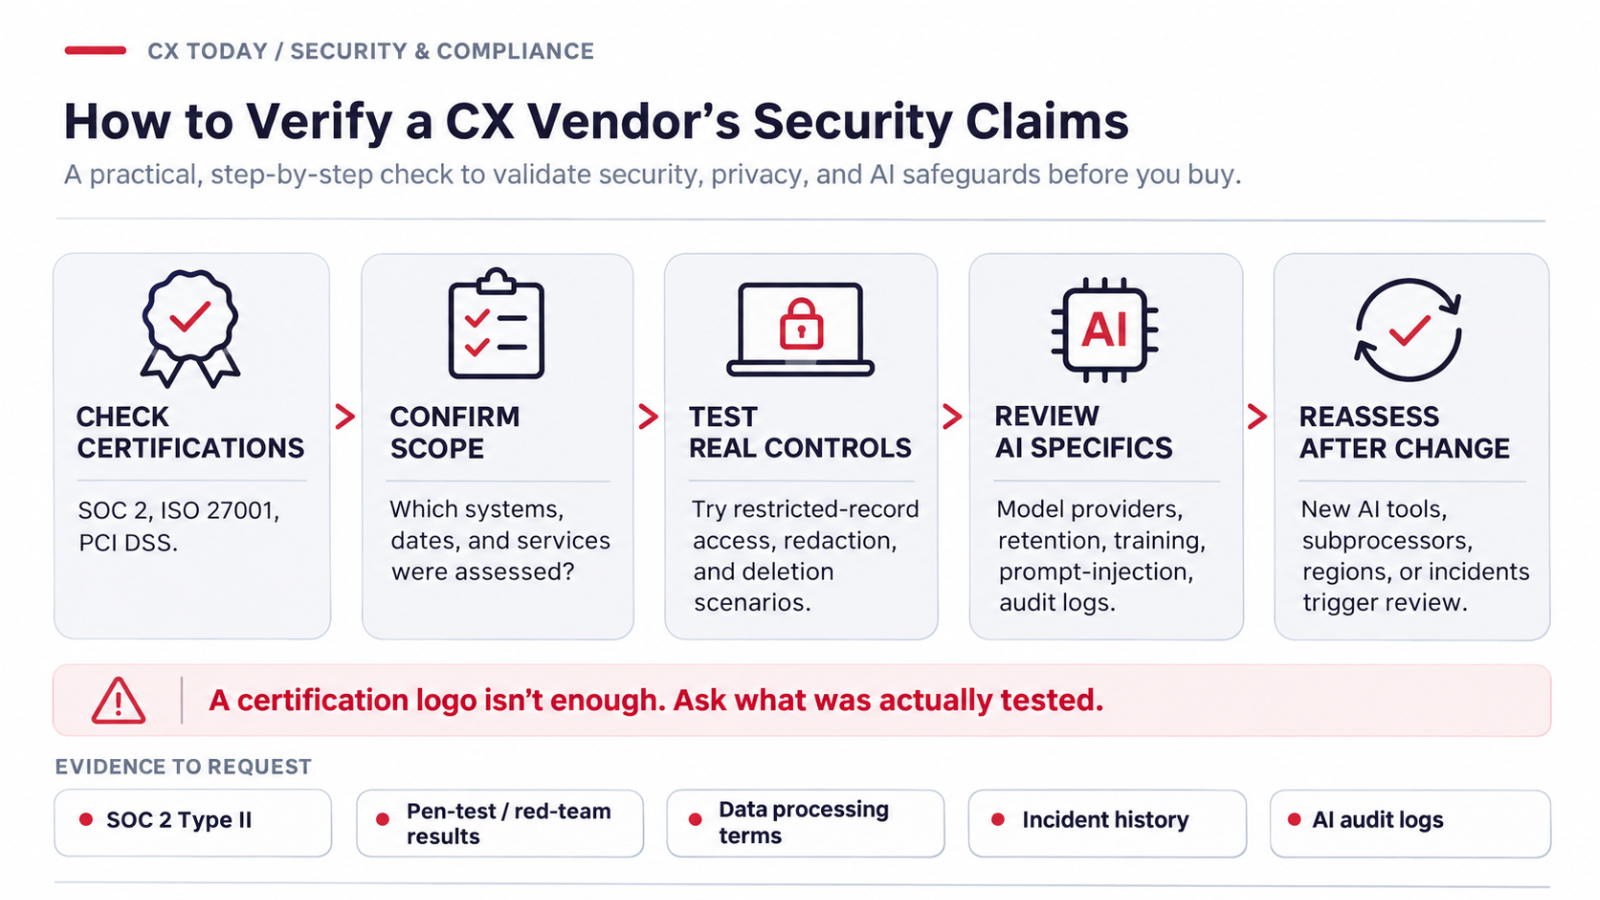

Any CX vendor could come to you with a fancy SOC 2 report, but that doesn’t necessarily mean it covers the AI voice agent you’re buying, the third-party tools processing customer conversations, or the CRM integration giving AI access to account records.
CX security and compliance is getting complicated, although frankly, it’s never been particularly straightforward. Every interaction generates voice recordings, transcripts, payment details, and behavioral data, which makes CX platforms some of the richest data environments in the enterprise, and some of the most exposed now that AI is in the mix.
IBM’s 2026 research found that 92% of organizations reporting an AI-related breach lacked proper AI access controls. Seems like we’re still putting the cart before the horse with AI-powered CX, which is problematic when, as Nik Kale, Principal Engineer of CX Engineering, Cloud Security & AI platforms at Cisco, told us:
“AI governance is moving out of the back office and into the customer journey.”
This CX security and compliance guide is here to help you rethink what vendors need to prove, and what buyers should refuse to take on trust.
Key Takeaways:
-
Follow the data: Find out where customer information ends up, who gets access, and when it’s finally deleted.
-
Challenge AI promises: “We don’t train on your data” leaves plenty of other privacy questions unanswered.
-
Question certifications: Find out exactly which systems the auditors examined.
-
Put security to the test: Ask vendors to show what happens when someone tries to access restricted records.
-
Watch for changes: Yesterday’s assessment won’t tell you what a newly added AI model can access.
What Do CX Security, Privacy and Compliance Cover?
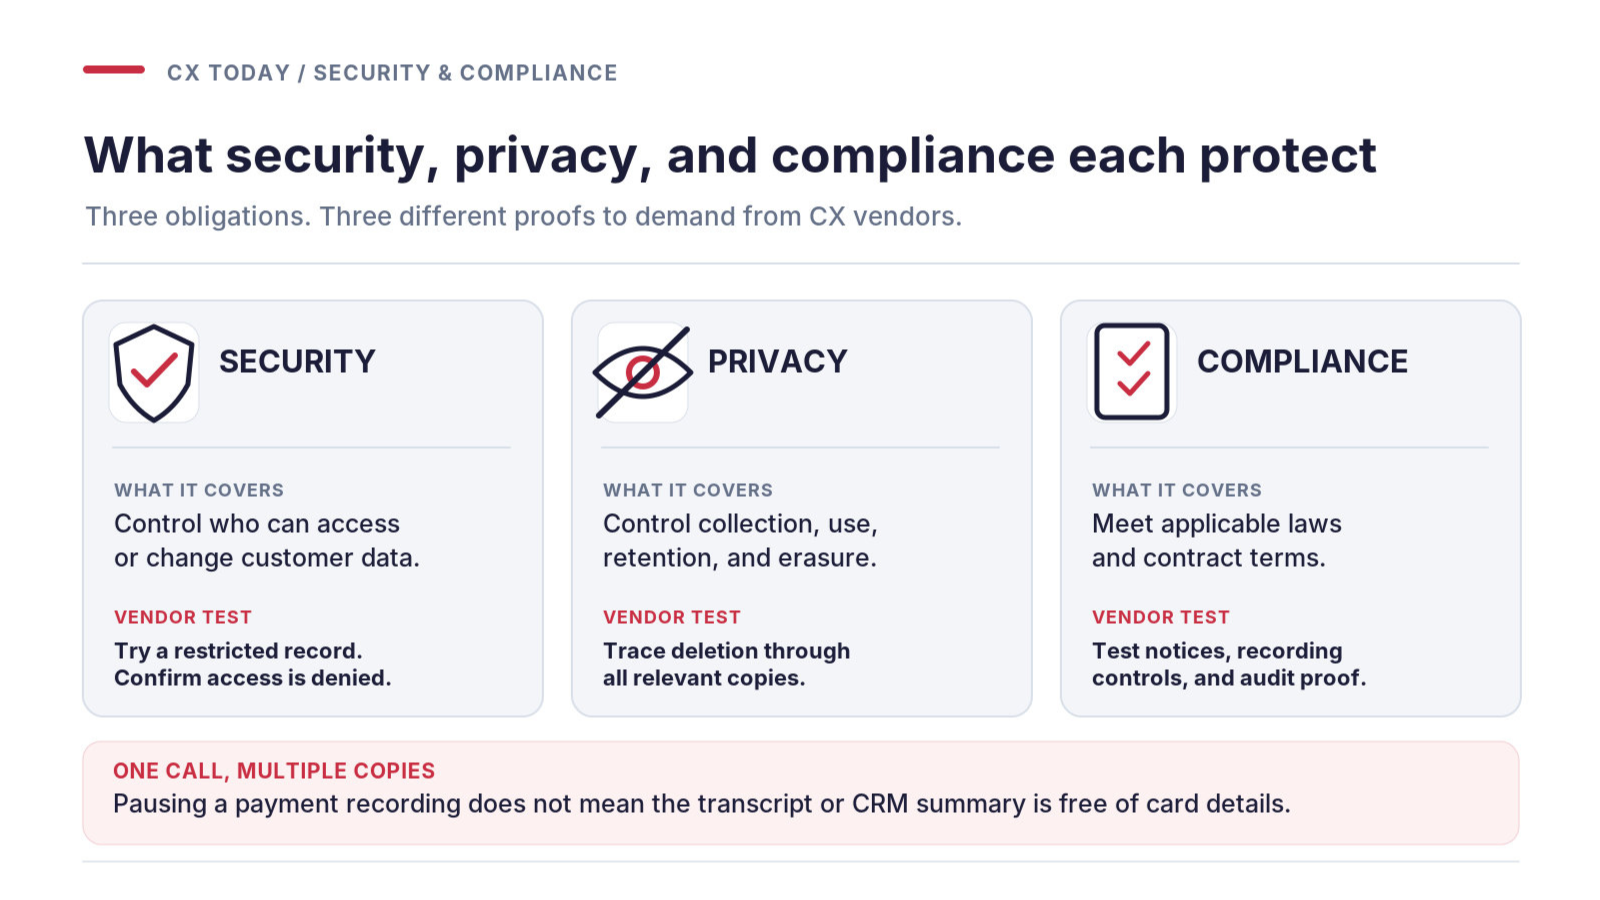
CX security, privacy and compliance are the interconnected elements that encompass the technical safeguards, legal frameworks, and operational policies used to protect customer data across all customer experience channels. This includes contact centers, digital engagement platforms, CRM systems, AI-driven tools, analytics platforms, and workforce management solutions. The whole thing.
|
Area |
What it means in practice |
A useful vendor test |
|---|---|---|
|
Security |
Restricting access to recordings and accounts, including AI tools using shared credentials. |
Try opening a record outside the employee or agent’s assigned permission. |
|
Privacy |
How much customer information gets collected, who uses it, and when it’s erased. |
Follow a deletion request beyond the original recording. What happens to transcripts and copies held elsewhere? |
|
Compliance |
The regulations and contract terms governing customer interactions. |
Check whether required notices appear, sensitive recordings are suppressed, and the system keeps proof. |
Picture a customer giving their card details to a support agent. The agent pauses the recording, following company policy. Fine, except the AI transcription tool might’ve captured everything anyway. An automated summary could even send those details into the CRM. One conversation, several copies of information that shouldn’t have been kept.
CX compliance reaches right into the agent’s working day. When should recording stop? What consent needs capturing? When should old transcripts disappear? Compliance tools can handle some of this automatically, but incorrect settings can leave sensitive information sitting exactly where it shouldn’t be.
Which CX Security and Compliance Regulations Apply?
Hopefully, you have an idea of the basics already, but it’s tricky, since regulations apply depending on who you’re serving and what your technology does. Some get surprisingly specific about everyday contact center activities, so have counsel check your actual service design against this map rather than relying on a vendor’s generic compliance claim.
|
Regulation |
Where CX teams can run into trouble |
Question worth asking |
|---|---|---|
|
EU GDPR |
The same customer information can sit in recordings, CRM records, analytics systems, and AI tools. Finding it all when someone exercises their privacy rights isn’t straightforward. |
Can the vendor trace every relevant copy of a customer’s data when an erasure request comes in? |
|
EU AI Act |
AI disclosure requirements under Article 50 apply from August 2, 2026, where relevant. Emotion recognition and certain content have their own rules. |
Can the vendor show exactly what customers are told about AI and when? |
|
UK GDPR / DUAA |
Customer data rights still apply, with updated complaints requirements under DUAA provisions in force by June 19, 2026. |
Can someone raise a privacy complaint during a support interaction? Where does it go, and who’s responsible for responding? |
|
California CCPA / Illinois BIPA |
Privacy rights and voice biometric processing can create obligations that ordinary call-recording notices don’t resolve. Some California ADMT requirements start January 1, 2027. |
Does the voice system create biometric identifiers, and how are relevant rights handled? |
|
Canada: PIPEDA / provincial laws |
Customer records can pass through processors in other countries while remaining subject to applicable privacy obligations. |
Who processes the information, where, and under which safeguards? |
|
PCI DSS / HIPAA |
Sensitive payment authentication data mustn’t be retained after authorization. Healthcare records require their own protections. |
Will payment details disappear from recordings and transcripts, and are the required healthcare terms in place? |
The trouble starts when these rules have to be applied across systems owned by different companies, and gets worse when AI keeps changing the rules.
It’s probably worth paying particular attention to voice AI right now, remembering that in 2026, Walmart and Lowe’s faced lawsuits alleging that their customer service systems captured voiceprints without meeting Illinois’ biometric privacy requirements. Those claims remain unproven, but they’re a good reason to check whether a vendor’s speech technology creates biometric templates. An ordinary call-recording notice won’t necessarily cover that.
Where Does Your Customer Data Actually Live?
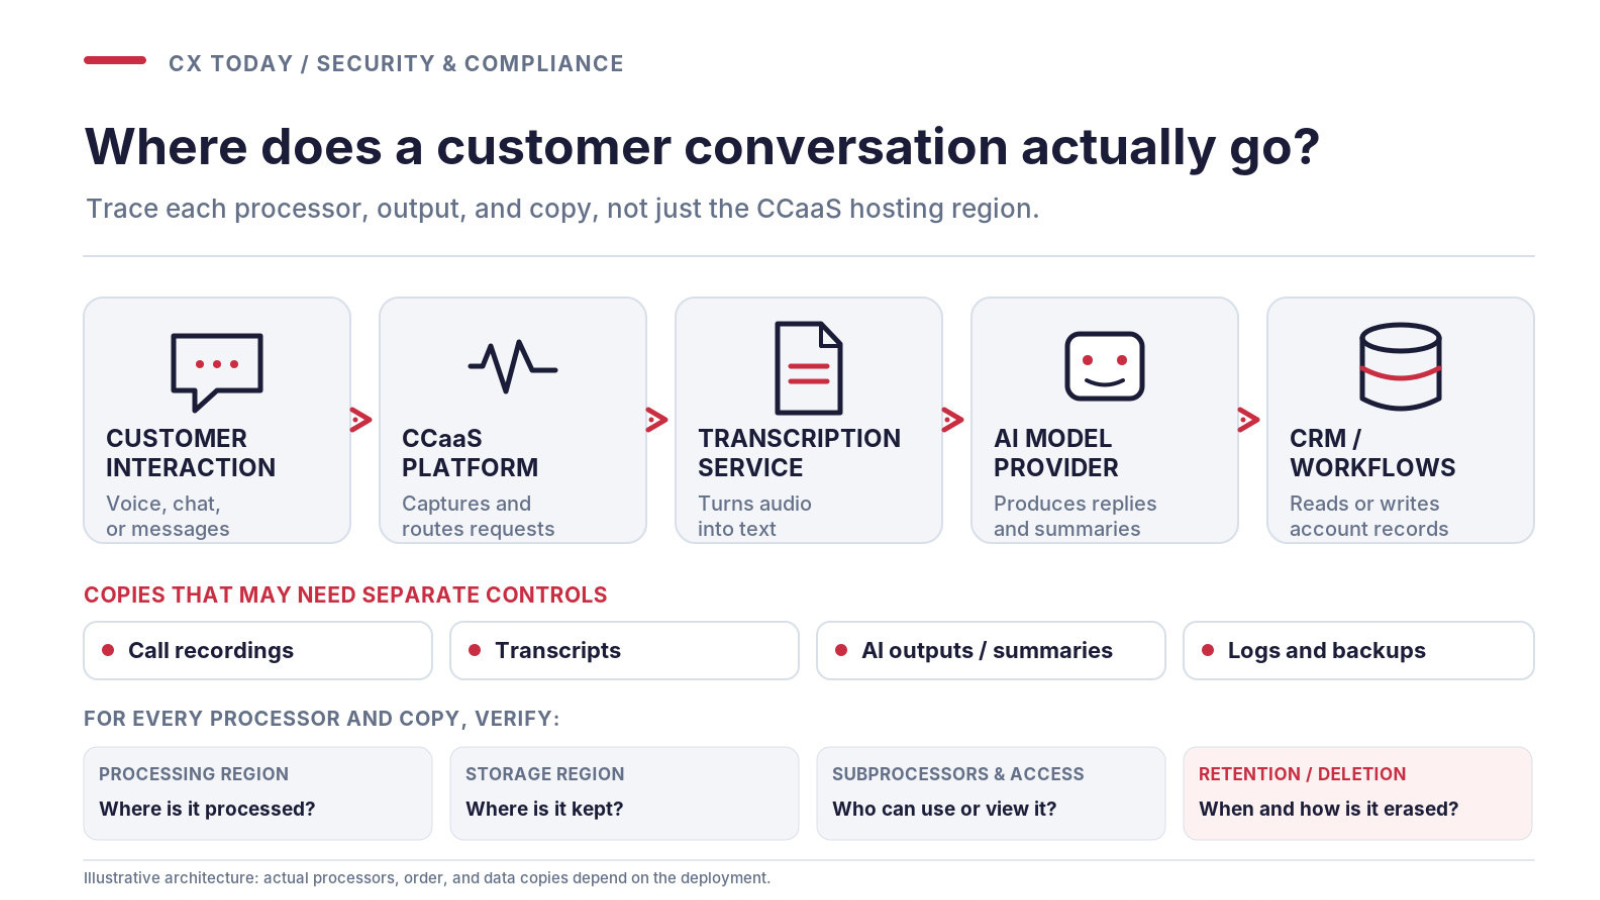
This is the first thing you should be ironing out if you need a CX security and compliance guide, and it’s also, oddly, something a lot of companies overlook.
In October 2026, Czech grocery company Rohlík discovered that attackers had stolen customer support records, including virtual assistant conversations, call transcripts, and uploaded files. Its payment and login systems weren’t affected. Unfortunately, some customers had already shared passwords or card details while asking for support, leaving the company with another problem to deal with.
That’s really what makes contact center data residency such a headache. A vendor says recordings stay in Frankfurt. Great, but who’s transcribing them? Where do AI summaries and troubleshooting logs end up? Can an overseas contractor open those records?
As Sean McConnell, GovTech Lead at Datactics, told us:
“Messy data increases exposure and makes those breaches harder to contain.”
Ask the vendor’s technical team to trace one complete customer interaction and show every copy of the information, including the ones the sales team rarely mentions. Then get these answers in writing:
-
For one complete interaction, where is each copy (recording, transcript, AI output, log, backup) stored and processed, and in which region?
-
Which subprocessors and model providers touch that interaction, and what notice do we get before one changes?
-
When a customer asks for erasure, which copies are deleted, by when, and what evidence do we receive?
-
At contract end, in what format do we get our data back, and when is it deleted on your side?
Encryption and access controls matter, of course. I’d still want someone to demonstrate that an unredacted transcript isn’t sitting in a debug log after the original recording has been deleted.
Is Your Customer Data Training Someone Else’s AI?
We’ve all seen the phrase: “We don’t train our models on customer data.”
That’s reassuring, until you see that the contract mentions retained prompts and human review. What happens when someone accidentally gives the bot their card number?
How contact centers protect data varies, and with AI, training, inference, and retention aren’t the same thing.
For instance, in September 2026, Anthropic reversed a 30-day retention requirement for certain models after discussions with more than 100 enterprise customers. Regulated businesses had pushed back. Clearly, these terms are worth negotiating.
Ask whether “no training” covers outside model providers, evaluation datasets, and support staff. Check when redaction happens, too. If card details disappear after transcription, have they already reached the model? What about the original audio and debugging logs?
Who Actually Has Permission to Access Customer Records?
Role-based access and activity monitoring only work if they apply to everyone, including the AI agents assisting your team.
An assistant connected to Salesforce shouldn’t inherit administrator permissions because someone took a shortcut during setup.
As ServiceNow’s Yevgeny Dibrov asked during an interview with us: